There’s a quiet tax on using AI to write code, and it isn’t the subscription. It’s that the model smart enough to understand your codebase is also the most expensive one to run — so every fix, every refactor, every small change gets billed at the top rate. shadcn/improve, a free agent skill from the creator of shadcn/ui, is built on a simple inversion of that problem: let the expensive model do the thinking once, and let the cheap models do the typing. It’s sitting at #4 on GitHub trending today, up 333 stars in a day to 10,454 total, and it’s one of the most practical AI dev tools to trend in a while — because the idea is obvious the moment you hear it, and the execution is more careful than the idea suggests.
The plan is the product
The tagline on the repo says it plainly: “Use your most capable model to audit your codebase and write plans for cheaper models to execute.” That’s the whole tool. You install it with npx skills add shadcn/improve, and it works in any agent that supports the Agent Skills format. Run /improve and the skill audits your codebase — nine categories, from correctness and security to performance, test coverage, tech debt, dependencies, developer experience, docs, and direction — with every finding carrying file-and-line evidence, an impact rating, an effort rating, and a confidence rating. Then it vets its own findings: an advisor pass re-reads every cited location, drops the false positives, and records the rejections. Then it prioritises by leverage — impact divided by effort, weighted by confidence — and writes one plan file per finding into a plans/ folder, plus an index with the recommended order.
The key design decision is what the skill refuses to do. It never modifies source code itself. The only files it writes are the plans. It never runs commands that mutate your working tree — read, search, and read-only analysis only. And it never reproduces secret values: it records locations and credential types, and recommends rotation. If you ask it to implement something, it declines and points at the plan. The plan is the product, and the product is a markdown file any agent — or a human — can pick up and follow.
That matters because the pitch only works if the plans are good enough for a weak model to execute. The skill is designed around that: every plan is self-contained, with all context inlined — file paths, code excerpts, conventions, verified build, test, and lint commands — and every step ends with a command and an expected output, a machine-checkable definition of done. There are explicit out-of-scope lists and stop conditions instead of letting a small model improvise, and each plan stamps the git commit it was written against, so drift can be checked mechanically later.
Eleven commands, one workflow
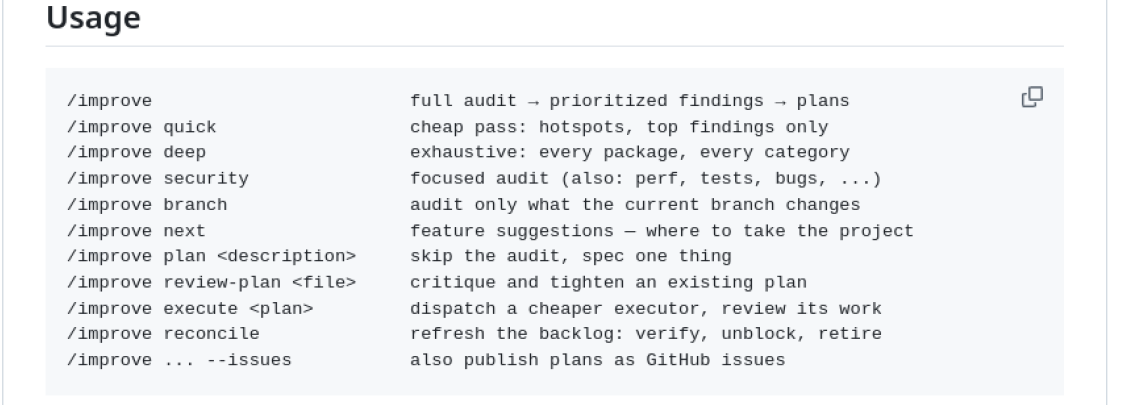
The skill ships with eleven commands, and they map to a workflow that feels like a small team rather than a single prompt. /improve runs the full audit. /improve quick does a cheap pass over hotspots and top findings only. /improve deep is exhaustive — every package, every category. /improve security runs a focused security audit, and there are focused variants for performance, tests, and bugs. /improve branch audits only what the current branch changes. /improve next suggests features. /improve plan <description> skips the audit and specs one thing directly. /improve review-plan <file> critiques and tightens an existing plan. /improve execute <plan> dispatches a cheaper model in an isolated git worktree, reviews its diff against the plan, and reports a verdict — approve, send back for up to two rounds, or block and refine. Merging always stays your call. And /improve reconcile refreshes the backlog next session: it verifies done plans, investigates blocked ones, refreshes drifted plans, and retires fixed findings. Add --issues and plans get published as GitHub issues with the same self-contained body.
The worked example in the README is a run against shadcn/ui itself, and it’s worth reading for what it shows about the vetting step. The audit found a shadow-config duplicated across search.ts and view.ts, with the copies already drifted — tech debt, medium effort, high confidence — and an O(n²) icon migration in migrate-icons.ts:168 — performance, small effort, high confidence. It also rejected a finding, with the reason recorded: an https_proxy environment variable flagged as an SSRF risk was by design, a standard proxy convention every CLI honours. That’s the kind of false positive that erodes trust in automated audits, and the skill’s answer is to show its working and its rejections rather than hide them.
What it costs, and the honest caveat
The skill itself is free — MIT licensed, installed with one command, no subscription, no API key required by the skill itself. It runs inside whatever AI coding agent you already use, so you pay that agent’s normal usage. The real cost is model usage: the audit runs on your most capable, usually most expensive, model, and execution runs on cheaper ones. That trade only saves money if your cheap executor is actually cheaper than running the strong model for everything — which is true in most setups, since the price gap between frontier and mid-tier models is large — and the plans still need human review before merging. The skill is explicit that merging stays your decision, and that the executor’s work gets reviewed against the plan before it comes back to you.
There’s a second caveat worth stating plainly: none of this has been independently benchmarked. The claim that the plans are executable by “the weakest plausible executor,” the claim that vetting drops false positives, the nine categories and the leverage ordering — all of that is the project’s own description of its design, not a third-party test. No independent review was found in this research pass. The repo is also young in a specific way: created June 10, 2026, 23 commits, zero releases, last commit two months ago, five open issues, twelve open pull requests. That’s normal for a skill repo — it’s a small set of files, not a product with a release train — but it means you’re adopting one person’s workflow, not a maintained platform. The author is shadcn, whose shadcn/ui component library is one of the most widely used in the React world, which is presumably why the repo has 10,454 stars and 427 forks despite being a single skill.
Don’t confuse it with Google Skills
If you read corei10.com regularly, you may remember Google Skills, the 186-skill catalog for Google Cloud we covered on November 6. Same “agent skills” theme, different thing entirely. Google Skills is a catalog — a library of skills you pick from, each one teaching an agent how to do a specific cloud task. improve is a single workflow skill: audit a codebase, write plans, hand them to cheaper models. You could, in principle, use both — one to run your cloud, one to clean up the code that runs on it — but they solve different problems, and improve is the one with the money-saving pitch. If you’re already using Claude Duet or Muse Spark Open for agentic work, improve slots into the same stack: the agent does the thinking, the plan does the talking, and the cheaper model does the typing.
Who should try it
The audience is narrow and that’s fine: developers with a codebase they actually work in, using an AI coding agent that supports the Agent Skills format. If that’s you, the install is one command and the first run costs you one audit on your best model. Start with /improve quick rather than the full audit — it’s the cheap pass, and it’ll tell you within minutes whether the findings are worth anything for your code. If the findings are mostly noise, you’ve spent one audit. If they’re real — duplicated config, an O(n²) loop hiding in a migration script, a security flag that’s actually by design — then the plans folder starts paying for itself, because every plan is a piece of work a cheaper model can now do without re-reading your whole codebase. That’s the bet: pay once for understanding, and never pay for it again.
Also today: November Pixel Drop: Pixel Tag, Gemini & More and Ring Drone Cam: $250 Flying Camera Ships Jan 27.
Leave a Reply